The Challenge
A US treatment facility urgently needed a modern software platform to manage substance use disorder (SUD) care. Beyond standard HIPAA compliance, handling SUD patient records carries significantly higher legal risk under 42 CFR Part 2, requiring strict consent tracking, row-level data isolation, and robust field-level encryption to prevent unauthorized disclosures.
The Choice
Brought on by a US substance use disorder treatment provider due to our deep healthcare compliance experience, we chose to prioritize security and infrastructure before building features. Rather than rushing user interface components, we invested the first weeks into establishing Infrastructure-as-Code (IaC) pipelines, field-level encryption models, and audit frameworks to ensure zero compromise on sensitive patient data.
What We Built
We engineered a secure, multi-tenant digital treatment platform:
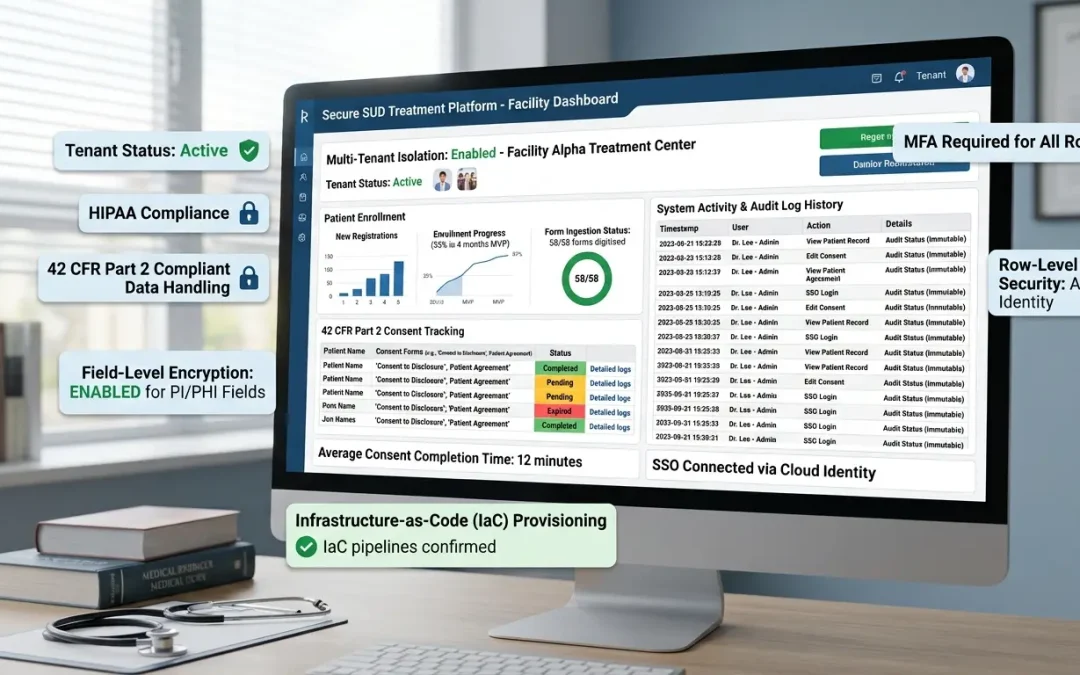
- Compliance Ingestion Engine: Converted 58 complex compliance and clinical forms into digital application workflows, enrollment modules, and monitoring tools.
- Field-Level Encryption & Security: Applied field-level encryption for high-risk attributes alongside row-level security across relational databases.
- Automated Cloud Infrastructure: Built serverless container environments behind private virtual networks, jump hosts, and Web Application Firewalls (WAF).
- Strict Authentication & Auditing: Enabled Multi-Factor Authentication (MFA), SSO capabilities, and immutable audit logging for every system action.
The Outcomes
- Tech Stack: React, Nest.js, Public Cloud (Private Virtual Network, Serverless Containers, WAF), Microservices Architecture, Infrastructure-as-Code (IaC) CI/CD, Relational Database with Row-Level Security, Multi-Tenant Architecture, MFA, SSO.
- Standards & Compliance: Built strictly to HIPAA and 42 CFR Part 2 standards; Field-level encryption, Role-Based Access Control (RBAC), and detailed audit logging.
- Delivery Velocity: Blank page to complete MVP in 4 months.
- Client Commitment: When client circumstances caused a project pause, we chose to build beyond the paid scope to bring the solution to a penetration-test and demo-ready stage—reflecting Rite Technologies' standard practice, where most of our partners trust us for between 5 and 10 years across their product lifecycles.
The Handover
The client’s team successfully ran demos themselves and achieved complete closure on all MVP requirements. The platform stands fully prepared for penetration testing and immediate launch whenever the client is ready to resume.
Tech Stack
React
NestJS
Microservices
Healthcare IT
HIPAA
42 CFR Part 2
Field Level Encryption
Row Level Security
Multi Tenant
IaC
WAF
Audit Logging
Substance Use Disorder Care
If you require rigorous regulatory compliance, consent tracking, and data security for sensitive care records,
let's review our compliance framework