The Challenge
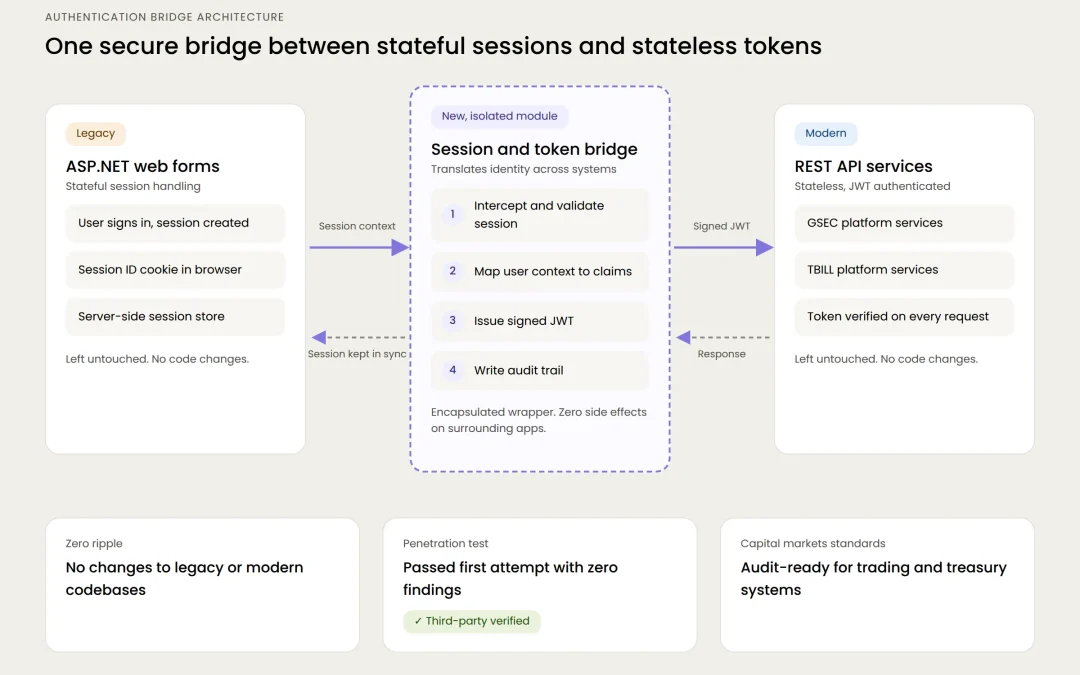
Following successful deliveries on their GSEC and TBILL platforms, the client presented an ongoing security challenge. Their technology ecosystem contained a mix of legacy ASP.NET web applications with traditional stateful session handling and newer services operating on stateless REST APIs using JSON Web Tokens (JWT). While each system functioned securely in isolation, user transitions between the legacy and modern platforms created potential session vulnerabilities and authentication friction.
The Choice
The client had been stuck on the architectural design for this cross-system bridge for some time. They needed an approach that would close the security gap completely, subject to a strict constraint: the solution had to integrate seamlessly without causing architectural ripples or requiring widespread refactoring across their broader codebase. We collaborated closely with their technical leadership to design a isolated, non-intrusive security bridge.
What We Built
We engineered a specialized authentication and session bridge module:
- Token & Session Mapping Layer: Intercepted and securely validated user context as traffic crossed between ASP.NET session stores and JWT-authenticated API services.
- Isolated Security Wrapper: Encapsulated the authentication translation logic into a dedicated component, ensuring zero side effects or structural changes to the surrounding applications.
- Audit-Ready Validation: Subjected the new architecture to stringent internal security reviews prior to formal third-party audits.
The Outcomes
- Tech Stack: ASP.NET, REST APIs, JSON Web Tokens (JWT).
- Security & Compliance: Built to enterprise capital markets standards; passed third-party vendor penetration testing on the first attempt.
- Client Trust & Partnership: Delivered as an extension of our ongoing work on GSEC and TBILL platforms—reflecting Rite Technologies' standard practice, where most of our partners rely on us for between 5 and 10 years to maintain and secure their mission-critical software assets.
The Handover
By closing the gap between old and new code without touching the rest of their platform, we eliminated a persistent security risk and gave the client full confidence in their cross-system authentication model.
Tech Stack
ASP.NET
REST API
JWT
Capital Markets
Financial Services
Penetration Tested
Session Management
Authentication
Security Bridge
If you need to bridge session management across legacy and modern systems without causing platform disruption,
let's talk.